
Vulnerability Templates
Vulnerability templates are reusable finding definitions that pre-fill common fields when creating new issues. They codify your organization's knowledge about known vulnerability types into a searchable library.
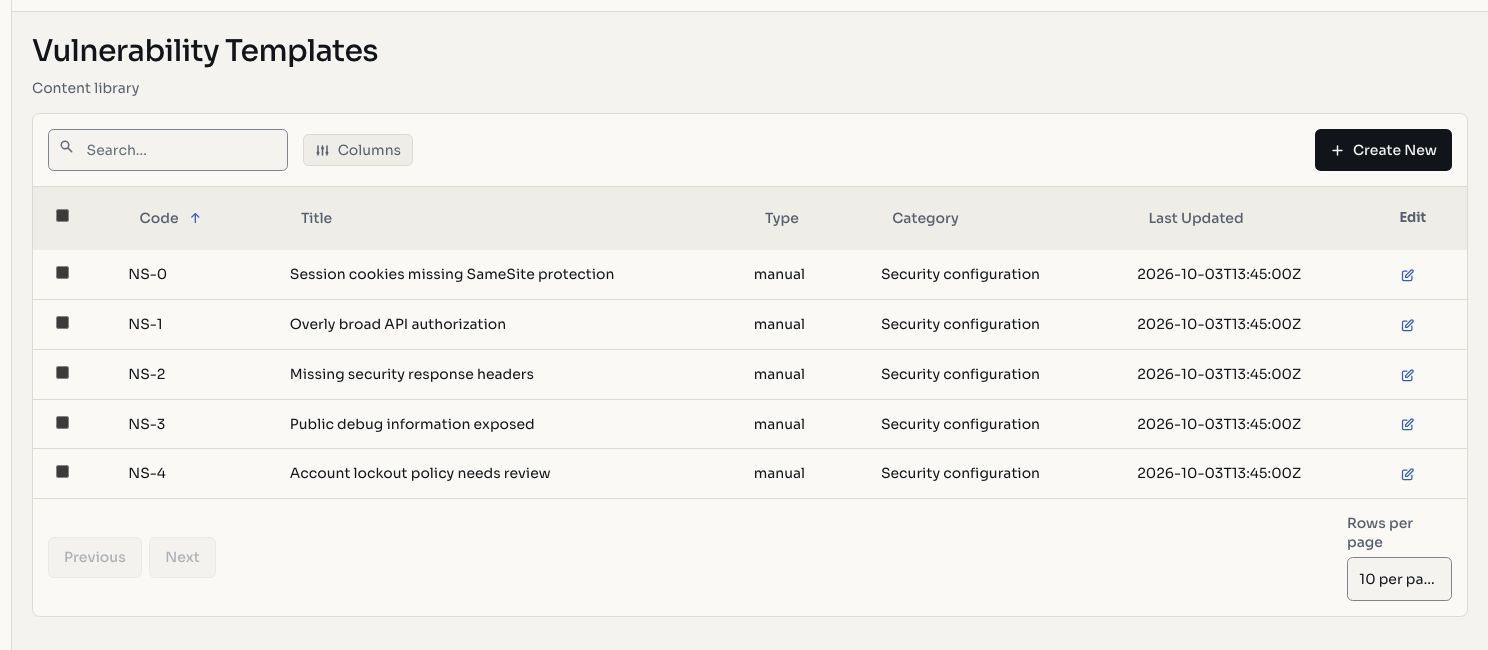
Screenshots use fictional demonstration data.
What's in a Template
| Field | Description |
|---|---|
| Title | Standardized vulnerability name |
| Description | Detailed explanation of the vulnerability |
| Severity | Default severity rating |
| CVSS v3.1 Score | Pre-calculated CVSS vector and score |
| Remediation | Recommended fix or mitigation steps |
| Category | Classification (e.g., injection, authentication, configuration) |
| References | Links to relevant standards, CVEs, or documentation |
Template Library
The template library provides:
- Search: find templates by keyword or title
- Filter: narrow by severity, category, or other fields
- Column selector: customize which fields are visible
- Pagination: browse large collections efficiently
Creating Templates
Manual Creation
Create templates from scratch by filling in each field. Useful for organization-specific vulnerability types.
AI-Assisted Generation
Describe a vulnerability in plain text, and Hashiro's AI generates a complete template including title, description, CVSS scoring, and remediation guidance.
TIP
AI-assisted generation is a fast way to seed your template library. Generate a draft, then refine the details to match your standards.
Using Templates
When creating a new finding in a project:
- Select a template from the library
- Fields are pre-filled with the template's content
- Customize any field for the specific instance (e.g., add target-specific evidence)
- Save the finding