
CVSS Scoring
Hashiro integrates the Common Vulnerability Scoring System v3.1 (CVSS) into every security finding. CVSS provides a standardized method for rating vulnerability severity and communicating risk.
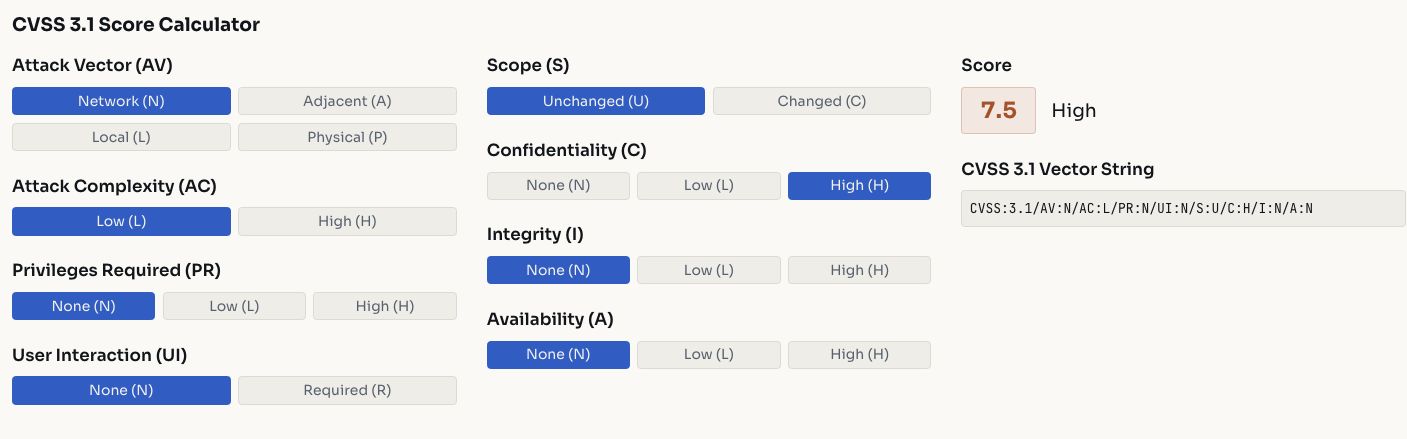
Screenshots use fictional demonstration data.
Score Calculator
The built-in calculator lets you set each vector component and automatically computes the overall score.
Exploitability Metrics
| Metric | Values | Description |
|---|---|---|
| Attack Vector (AV) | Network, Adjacent, Local, Physical | How the vulnerability is exploited |
| Attack Complexity (AC) | Low, High | Conditions beyond the attacker's control |
| Privileges Required (PR) | None, Low, High | Access level needed before exploitation |
| User Interaction (UI) | None, Required | Whether a user must take action |
Scope
| Metric | Values | Description |
|---|---|---|
| Scope (S) | Unchanged, Changed | Whether exploitation impacts resources beyond the vulnerable component |
Impact Metrics
| Metric | Values | Description |
|---|---|---|
| Confidentiality (C) | None, Low, High | Impact on information disclosure |
| Integrity (I) | None, Low, High | Impact on data modification |
| Availability (A) | None, Low, High | Impact on service availability |
Severity Classification
The CVSS score maps to a severity level:
| Score Range | Severity |
|---|---|
| 9.0 - 10.0 | Critical |
| 7.0 - 8.9 | High |
| 4.0 - 6.9 | Medium |
| 0.1 - 3.9 | Low |
| 0.0 | Informative |
Vector String
Each assessment produces a vector string encoding all metrics in a compact format:
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:HThis string is stored with the finding and included in reports.
How CVSS Is Used in Hashiro
- Prioritization: findings are ranked by score in project views and dashboards
- Reporting: scores appear alongside each finding in PDF reports
- Dashboard metrics: severity breakdowns derive from CVSS classifications
- Remediation planning: the effort matrix combines severity with remediation complexity