
External Attack Surface Management (EASM)
EASM gives you continuous visibility into your organization's internet-facing assets. Hashiro automatically discovers subdomains, services, and URLs, then probes and monitors them for changes, vulnerabilities, and misconfigurations.
EASM is a core pillar of Hashiro's Continuous Threat Exposure Management (CTEM) approach: rather than point-in-time assessments, your attack surface is monitored on an ongoing basis so new exposures are detected as soon as they appear.
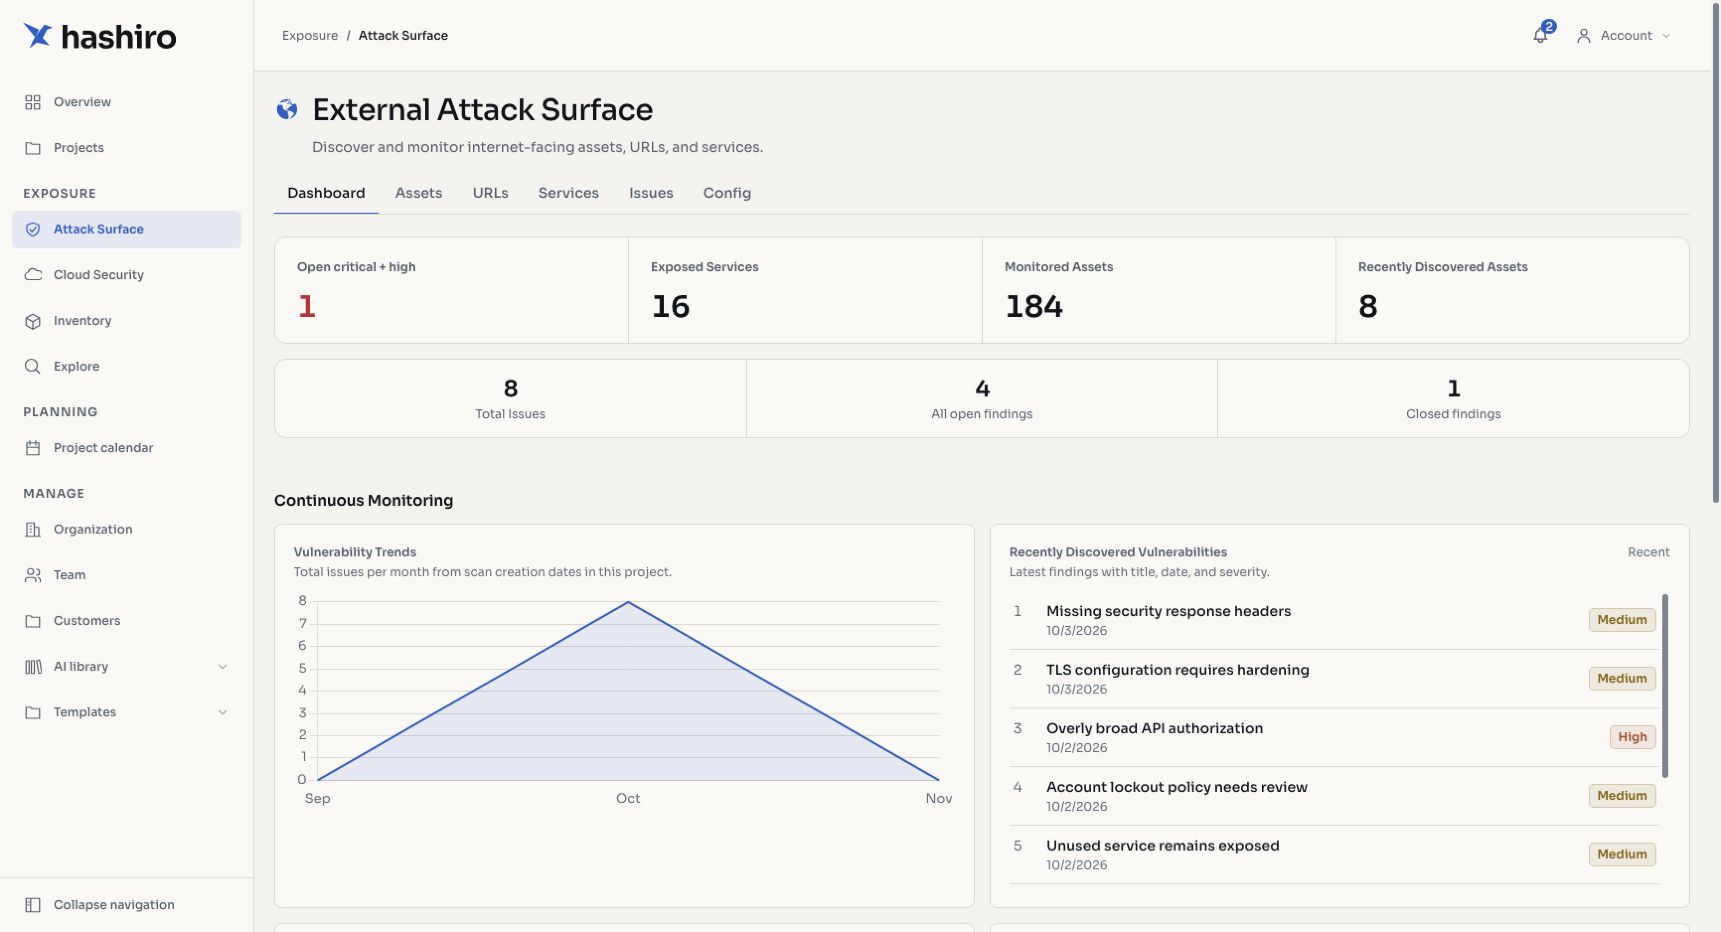
Screenshots use fictional demonstration data.
How It Works
- Scope Definition: you define in-scope and out-of-scope targets (domains, IPs, CIDRs, wildcards).
- Automated Discovery: Hashiro enumerates subdomains, crawls for URLs, and scans for open services.
- Probing: each discovered asset is probed with HTTPX to collect metadata (HTTP status, page title, technologies via Wappalyzer, screenshots, favicon hashes, web server identification, CDN detection, and more).
- Vulnerability Scanning: Nuclei templates run against discovered assets to detect known vulnerabilities, misconfigurations, and exposures.
- Continuous Monitoring: monitoring repeats according to the service configuration. New assets, removed assets, and status changes are tracked.
Module Tabs
The EASM module is organized into six tabs:
| Tab | Purpose |
|---|---|
| Stats | Summary statistics for the entire attack surface |
| Assets | Paginated list of all discovered assets with probe data, screenshots, and technology details |
| URLs | Discovered URL paths with probe information |
| Services | Exposed network services detected via port scanning |
| Issues | Vulnerabilities and misconfigurations found on the attack surface |
| Config | Included scope and exclusions |
Key Capabilities
- Asset Discovery: automated subdomain enumeration and asset identification
- HTTP Probing: rich metadata collection for every web-facing asset (title, headers, status codes, technologies, screenshots)
- Port Scanning: detection of exposed services across 27 standard ports
- Vulnerability Detection: Nuclei-based scanning for known CVEs, misconfigurations, and exposures
- Screenshot Capture: visual snapshots of every web asset for quick identification
- Technology Detection: Wappalyzer-powered fingerprinting of web technologies, frameworks, and libraries
- CDN Detection: identification of CDN providers fronting your assets
- Change Tracking: monitor asset availability, technology changes, and new exposures over time
- Export: download asset data as PDF or CSV
TIP
EASM availability and monitored-asset limits depend on your organization's provisioned service and license.
Related Features
- Cloud Security: monitor cloud infrastructure alongside your external surface
- Inventory: cross-project asset search across all your assets
Navigate the surface view
- Open Attack Surface in the sidebar.
- Use Stats for the overview, Assets for hosts, URLs for paths, and Services for ports.
- Open a row to inspect its evidence and associated findings.
- Use Issues to filter findings and Config to review scope.
The view is limited to the organization you are allowed to inspect. Empty results can mean no in-scope targets or no collected data yet. See Scope configuration.